copiiot.com: A Copilot Lookalike Where One Capital Letter Does the Work
copiiot.com was registered on 25 October 2026. Written with a capital I, it reads as Copilot. Here is how the trick works, what we found, and how to stay ahead of it.
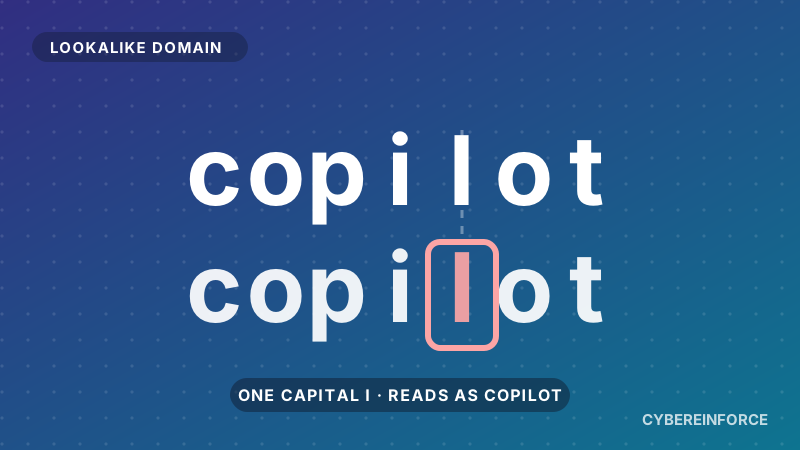
Read this out loud: copiIot.com. Most people see "Copilot". Look again. The first line below is the real name. The second has a capital I where the l should be.
copiIot
In most sans serif fonts, a capital I and a lowercase l are almost the same plain vertical bar. Change one letter, keep the rest of Microsoft's product name exactly as it is, and the eye finishes the word on its own.
Why the capital letter matters
The domain that was actually registered is copiiot.com, with two lowercase i's. Domain names are not case sensitive, so copiIot.com and copiiot.com point to the same place. That is the whole trick. An attacker does not need the address bar to look right. They only need the text around it to look right: the display text of a link in an email, a line in a chat message, a caption under a QR code, a footer in a document.
In that text they can write the name with the capital I, and the person reading it sees Copilot. The link underneath goes to the real registration. Once the page opens, the browser shows the lowercase form, and by then the reader has already decided where they are.
The timing is not an accident either. Copilot is the product name people are being asked to trust inside their own companies right now, so an invitation, a shared file or a sign in prompt that mentions it does not feel unusual.
What we found
Cybereinforce flagged the domain as an imitation of Copilot. This is the registration data.
| Detail | What we saw |
|---|---|
| Domain | copiiot.com, imitating Microsoft Copilot |
| Registered | 25 October 2026 at 14:21 UTC, two days before this post |
| Expires | 25 October 2027 |
| Registrar | Wix.com Ltd. |
| Nameservers | NS1.ATOM.COM, NS2.ATOM.COM |
| Registry status | client transfer prohibited, client update prohibited. Not suspended at the time of writing |
| Last changed | 26 October 2026 at 10:42 UTC |
We are treating copiiot.com as an impersonation domain because of how the name was built and how new it is. We will update this post if we see how it is put to use.
Why a two day old domain is a problem
Reputation lists and vendor ratings only know what someone has already reported. A domain that is two days old has no history, so it looks clean to every list. Attackers rely on exactly that window. A fake sign in page needs only a web server, a fake invitation needs only a mailbox, and both can be live within minutes of registration.
We watch the entire WWW and protect you before you get hit, as well as your brand.
- Registered.
copiiot.comwas created on 25 October 2026 at 14:21 UTC. - Changed. The record was updated on 26 October 2026 at 10:42 UTC.
- Flagged by Cybereinforce. The name was identified as a Copilot imitation and blocked in the browser while the registrar and Microsoft are informed.
How to spot it
- Do not trust display text. Hover over a link and read the real address before you click.
- Count the letters. A real Copilot name has an l. If the address shows two i's in a row, it is not Copilot.
- Open Copilot yourself. Use your Microsoft 365 app or your own bookmark, not a link that arrived in a message.
- Be careful with sign in prompts that start from a message. If a page asks you to sign in after you followed a link, stop and report it.
Indicators
| Type | Value | Note |
|---|---|---|
| Domain | copiiot.com | Copilot lookalike, also written copiIot.com in display text |
| Nameserver | NS1.ATOM.COM, NS2.ATOM.COM | Context only. These are shared infrastructure, so do not block them |
Your own brand uses the same trick against you
Copilot is the example, but a capital I for an l works on any company name that has one. Your suppliers and customers know your domain, and a domain one character off is enough to send them a fake invoice with new bank details. With Brand Protection, your own domain and company name are watched in every spelling that matters. We described a similar case in a Microsoft lookalike we took down earlier this month, and our newly registered domain monitoring is what catches domains like this one on the day they appear.
How you would be protected with Cybereinforce
- Lookalikes are found early. Swapped letters, extra characters and lookalike glyphs such as I and l are caught, not only exact copies of a brand name.
- The browser block protects people right away. A takedown takes time, and enforcement in the browser does not wait for it.
- New domains get no free pass. A domain that is two days old is treated with the caution its age deserves.
- Your own brand is watched, and you hear about each lookalike through Microsoft Sentinel and email straight away.