A Microsoft Lookalike Domain, Caught and Taken Down by Cybereinforce
rnicrosofte.com copied Microsoft's name with an r and an n in place of the m. Cybereinforce detected it, coordinated with Hostinger, and took it down the same day. Here is what we saw and why it matters for your brand.
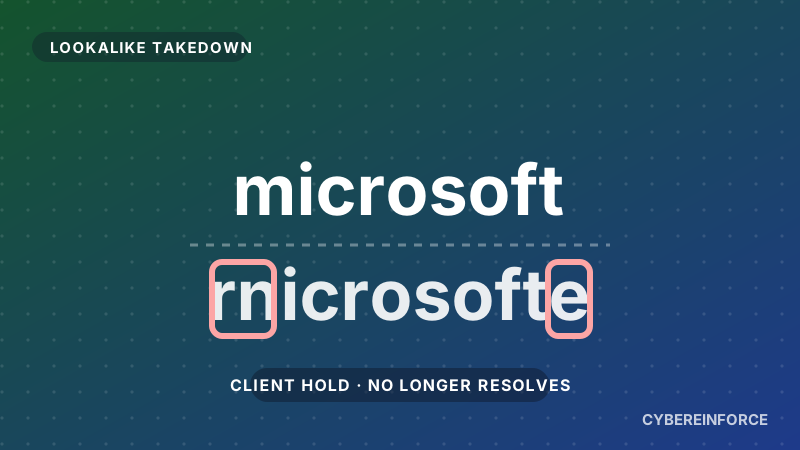
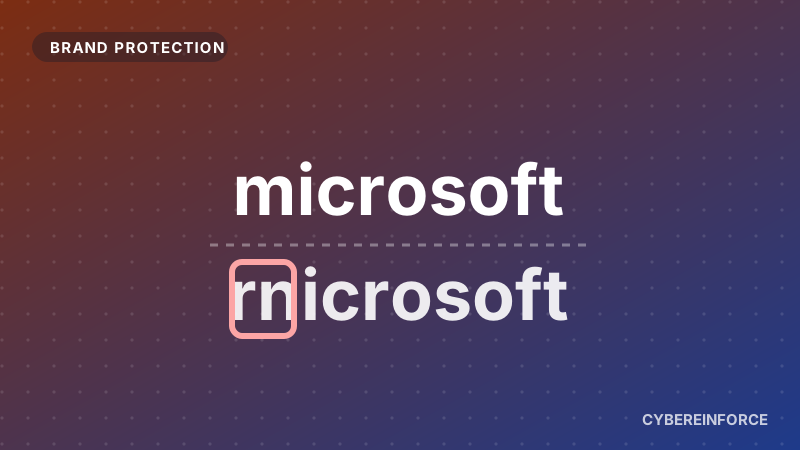
Read this domain out loud: rnicrosofte.com. Most people see "microsoft". Look again. The "m" at the start is an "r" and an "n" standing very close together, and an extra "e" has been added at the end. On a phone screen or in a busy inbox, nobody checks.
A lookalike domain does not have to fool a security tool. It only has to fool a person for two seconds, long enough to type a password or approve a payment.
What we found
Cybereinforce flagged the domain and we opened a takedown case on 14 October 2026. This is what the case looked like.
| Detail | What we saw |
|---|---|
| Domain | rnicrosofte.com, imitating Microsoft |
| Registered | 17 December 2025 |
| Registrar | Hostinger |
| Nameservers | Cloudflare |
| Case opened | 14 October 2026 |
| Registry status | client hold, set on 14 October 2026 at 23:03 UTC |
| DNS today | No website address, no nameservers, no mail servers |
How the takedown played out
- Detected. Our watch flagged the domain as an imitation of Microsoft, based on the swapped letters and the added character.
- Case opened. We opened the case on 14 October 2026 with the registrar and registry details collected.
- Coordinated with Hostinger. We worked directly with Hostinger, the registrar, to get the domain suspended.
- Taken down by Cybereinforce. The registry status changed to client hold at 23:03 UTC the same day, and the domain dropped out of DNS.
Cybereinforce took this domain offline. A client hold means the registrar has suspended the domain. It is pulled out of the .com zone, so the website, the nameservers and the mail servers all stop answering. We keep checking every open case against the registry status, DNS and the website itself, and the registry status is the signal we trust most.
Who else saw it?
To our knowledge, Cybereinforce was the only security vendor that detected rnicrosofte.com. This is the pattern we describe in our threat intelligence write up: human analysts and automatic brand imitation signals are often early, and reputation lists catch up later, if they catch up at all.
Why a quiet lookalike is still a threat
This domain was registered ten months before we acted on it. That is normal. Attackers register lookalikes in bulk, let them age, and switch them on when a campaign is ready. A fake login page needs only a web server and a fake invoice needs only a mailbox, and both can be live within minutes.
Waiting for a victim to report a domain is the wrong model. Lists and reputation scores only know what someone has already seen, and a lookalike that has not been used yet looks clean to every one of them.
We watch the entire WWW and protect you before you get hit, as well as your brand.
Your own brand is a target too
Microsoft is the example, but the same trick works on any company name. Your suppliers and customers know your domain, and a domain one letter off is enough to send them a fake invoice with new bank details. With Brand Protection, your own domain and company name are watched in every spelling that matters. When a lookalike appears:
- it is checked and, when it is new or already known to be malicious, blocked for every Cybereinforce user
- you get a Microsoft Sentinel incident with the lookalike domain as its entity
- your administrators get an email the moment it is found
How you would be protected with Cybereinforce
- Lookalikes are found early. Swapped letters, extra characters and lookalike alphabets are caught, not only exact copies of a brand name.
- The browser block protects people while a takedown runs. Takedowns take time, and enforcement in the browser does not wait for them.
- Your own brand is watched, and you hear about each lookalike through Sentinel and email straight away.
- Takedowns are followed through. We coordinate with registrars and confirm the result from the registry, DNS and the website.