Our Threat Intelligence: Catching Phishing Domains Before Other Vendors Do
More than once we have blocked a phishing domain while the major security vendors still rated it clean. Here is how our threat intelligence works, why speed matters so much against modern phishing kits, and what that means for the people we protect.
There is a moment in every phishing campaign that decides how many people get hurt. It is the gap between the minute a malicious site goes live and the minute security tools start blocking it. For many campaigns that gap is measured in hours or days. Most of the damage happens inside it.
Our threat intelligence exists to make that gap as small as possible. And on several occasions, which we recorded on video, we had a domain blocked while it still showed up as clean with every major security vendor. In one case we were nine days ahead.
Why the first hours matter so much
Modern phishing kits do not just steal a password. They sit between the victim and the real Microsoft or Google login, capture the session after MFA, and pass it to the attacker in real time. One click can be enough to lose a mailbox.
How big is this? When Microsoft, Europol and their partners disrupted Tycoon 2FA in March 2026, that one kit was linked to an estimated 96,000 victims since 2023, and to tens of millions of phishing emails a month. Its successors and competitors are still out there, sold as a service, so new campaigns start every day on fresh infrastructure. The people running them know that reputation lists will catch up eventually. Their whole business is to be faster than that.
How our intelligence is built
- We watch live. Our analysts follow fresh phishing and malware infrastructure as it appears in public scanning feeds, in suspicious links we observe and in reports from our customers.
- A person looks at it. New findings are reviewed by analysts before they go into the shared feed. Size is easy. Being right is what counts, because a false block costs you trust.
- It goes out immediately. Fresh findings get the highest priority in the feed, ahead of our large historical database, so they reach every protected browser right away.
- The browser blocks it. The next person who clicks that link sees a block page instead of a fake login.
Enterprise customers can also send us a link they are unsure about. An analyst investigates it, and if it is malicious it is blocked for that customer automatically.
Seeing it happen
We do not want you to take our word for it. So we recorded several of these cases as they happened: the domain, what the security vendors said about it at that moment, and what happened next. Here are four of them.
Case 1: zero out of 94, then four vendors within hours
The domain paydomainlater[.]com was about nine months old and looked spotless. Zero detections out of 94 security vendors, a neutral community score. Our intelligence was the only source rating it as malicious. We published our finding to the security community, the domain was analysed again, and within hours four vendors started detecting it as malicious.
April 2026: Cybereinforce flagged the domain first, four vendors followed within hours.
Case 2: six days ahead of 17 vendors
We marked a phishing domain as malicious while it still had no detections anywhere. It stayed that way for days. Six days later, within a single afternoon, 17 security vendors flagged it as malicious or phishing, including names like BitDefender, ESET, Fortinet, Kaspersky and Sophos. Our customers had been protected the whole time.
April 2026: six days before vendor consensus.
Case 3: nine days earlier than the industry
On 17 April 2026 we blocked a domain that was only one month old. At that moment not a single vendor detected it. Five days later, still nothing. On 26 April, eleven vendors finally classified it as malicious. That is nine days in which anyone relying only on reputation would have been exposed.
April 2026: blocked nine days before eleven vendors caught up.
Case 4: an old domain is not a safe domain
This one is our favourite, because it breaks a common assumption. The domain was registered in November 2022 and looked clean for three and a half years. No vendor ever flagged it. On 15 April 2026 our intelligence blocked it. Today three other vendors agree that it is malicious. Attackers buy or take over aged domains exactly because people trust them, so age alone is never proof of safety.
Clean for 3.5 years, blocked by Cybereinforce first.
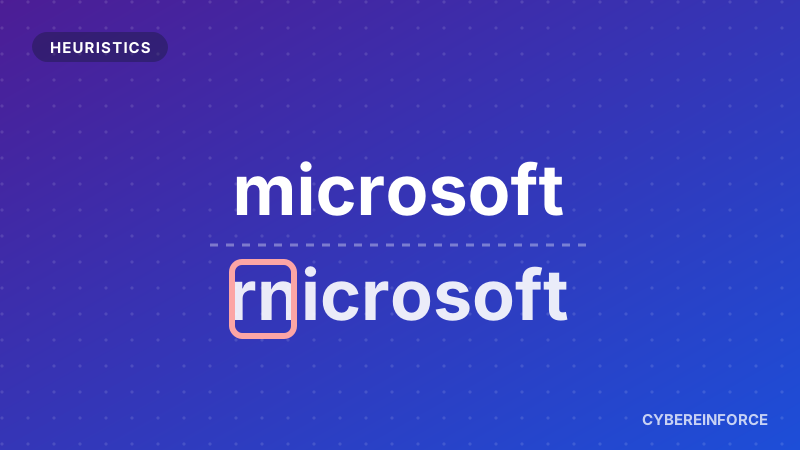
This is not luck. Combine human analysts watching live infrastructure with automatic signals like domain age and brand imitation, and you are simply early more often. You can find more of these breakdowns on our YouTube channel.
Not only fast, also careful
An aggressive feed that blocks real business sites is worse than useless. So we regularly clean our data against lists of the most popular legitimate websites, keep a global allow list for services that must never be blocked, and let your administrators allow anything for their own organisation in seconds. We also separate what is clearly malicious from what is only suspicious: malicious sites are blocked, suspicious ones show a warning and let the user decide.
How you would be protected with Cybereinforce
- You benefit from our findings within minutes, not after the rest of the industry has caught up.
- No feed to buy or maintain. On Corporate and Enterprise plans our curated intelligence works on top of your own rules and your Defender indicators.
- Every protected browser counts. Chrome, Edge, Firefox and Safari on desktop and mobile get the same intelligence at the same time.
- Everything is explainable. Each block tells your SOC which indicator matched and why.
Read more about every detection layer on our Threat Intelligence & Detections page.