Free IOC Lookup: Fresh Threat Intelligence for Every Investigation
Paste a domain or URL and get the same verdict that protects Cybereinforce customers' browsers, including domains our own watch caught before anyone else. Free for every analyst, with more for the community.
Every analyst knows the moment. A user reports an email. A sign in log shows a domain nobody recognises. A ticket arrives with a link and one question: is this bad?
Most reputation services can only answer once enough people have already reported the site. Phishing domains don't wait for that. Many of them are registered, used and abandoned within a day. So today we are opening up our own threat intelligence to every security professional, for free: the Cybereinforce IOC Lookup.
What it does
You paste one domain or one URL. Defanged indicators straight from a report, such as hxxps://evil[.]com, are cleaned for you. A moment later you see exactly what Cybereinforce would do if one of our customers opened it in their browser:
- Block when it is malicious, together with a preview of the block page your users would see.
- Warn when it is suspicious, so the user stops and thinks before going further.
- Open when our intelligence and our live checks have nothing against it right now.
A URL on a domain we block is reported as malicious, because Cybereinforce blocks the whole domain, not just one path.
Intelligence you won't find everywhere else
A large part of what Cybereinforce blocks is caught by our own sources first: our certificate transparency watch, our monitoring of newly registered domains, our analysts and the browsers our customers protect every day. Plenty of those domains are blocked by us long before they show up anywhere else.
Until now, only our customers benefited from that. With the IOC Lookup, those verdicts are available to you during your own investigations, one indicator at a time.
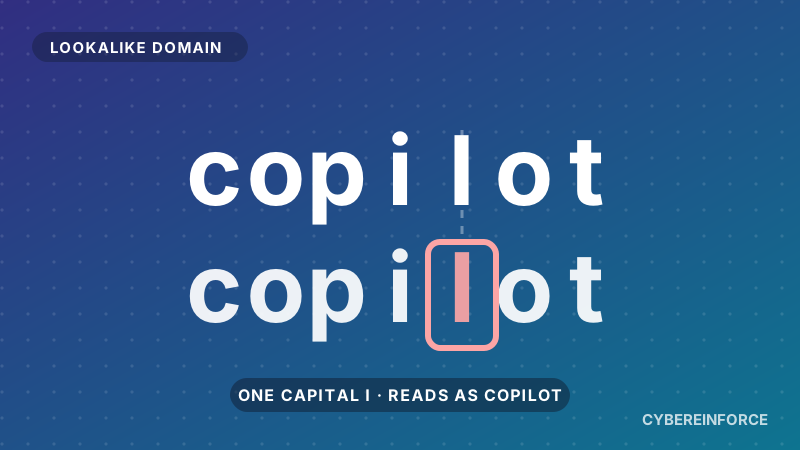
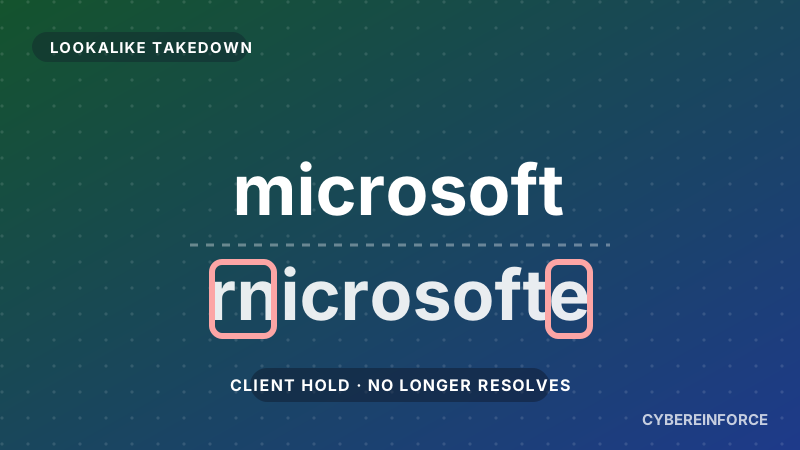
Take a current example. On 25 October someone registered copiiot[.]com. Written with a capital I, it reads as Copilot in an email or a chat message. We wrote about it two days later. Look it up today and the answer is immediate: malicious, blocked.
Day zero checks for what nobody has reported yet
A domain we have never seen before is not simply waved through. It goes through the same checks our browser protection runs live: brand lookalikes, newly registered domains, machine generated names and the link shapes phishing kits use. That is how a site registered this morning can already be flagged this afternoon.
Anything new goes to the Cybereinforce analysts as well. Leave your email address with a lookup and we'll send you their verdict.
One more source for your investigations
The IOC Lookup is built to sit next to the tools you already use. Reach for it when you:
- triage a reported phishing email and need a fast second opinion on the link,
- enrich a Defender or Sentinel incident with an independent verdict,
- check an unfamiliar domain that showed up in sign in or proxy logs,
- want to be sure before they allow a site that a user is asking for.
Every answer is a fresh data point from a team that spends all day hunting the domains attackers registered this week.
Free for everyone, more for the community
For anyone. No signup, no account, just paste and look up.
For community members. Sign in with your Microsoft work account, join our weekly threat newsletter and also see the reasons behind every verdict.
For Cybereinforce client administrators. Just sign in, no joining needed.
Members can also ask for a short list every morning: ten malicious domains to block that day, mostly brand impersonation, ready to paste into Defender.
Built with the community, for the community
The response from the security community to our free tools has been incredible, and this one is our way of giving back. Right under every result you can report a false positive, suggest a different category or ask us to block something. Cybereinforce analysts review every request and reply by email.
Every lookup of something new, every correction and every block request makes the intelligence sharper, for you, for every other analyst and for every browser we protect. Thank you for being part of it.
How you would be protected with Cybereinforce
- Every lookup, automatically. The IOC Lookup shows one verdict at a time. Cybereinforce customers get the same check on every site every user opens, in every browser, with no limit.
- Blocked before a password is typed. Malicious sites are stopped at the page load, and suspicious ones show a warning first.
- Day zero, not day three. Lookalikes like
copiiot[.]comand freshly registered domains are caught by live checks, before they appear in public feeds. - Built for Microsoft Defender environments. Deploy across Chrome, Edge, Firefox and Safari in minutes. Start a free 14 day trial.
Ready? Open the free IOC Lookup and try your next indicator.